Announcements - Latest News

Record 769 arrests and USD 65 million in illicit pharmaceuticals seized in global bust

Wednesday, 2 July 2025

An INTERPOL-coordinated operation across 90 countries has resulted in the seizure of 50.4 million doses of illicit pharmaceuticals worth USD 65...

More ›››

Strengthening the fight against cybercrime

Thursday, 23 January 2025

The need to strengthen the capabilities of the Cybercrime Sub-Directorate regarding the fight against and prevention of crimes and/or anti-social...

More ›››

57 men arrested for possessing and sharing over 100 000 depictions of child sexual abuse

Wednesday, 13 March 2024

The Cyprus Police - Cybercrime Subdivision, actively participating in the actions of Europol, after training received by its members, in relation to...

More ›››

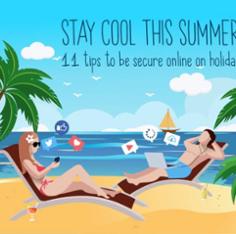
Stay cool this summer - 11 tips to be secure online on holiday

Wednesday, 9 August 2023

Summer holidays are a chance to relax, but they can be a source of high stress themselves if you are not safe online. To help with this, the European...

More ›››

Europol's 9th Internet Organised Crime Threat Assessment (IOCTA) has been released

Wednesday, 19 July 2023

Forget the cliché of a solitary figure in a hoodie hunched over a keyboard in a dark room crunching lines of codes. It is an image that no longer...

More ›››

Six sexually-abused children rescued as a result of Europol Victim Identification Taskforce

Friday, 26 May 2023

Six victims of child sexual abuse have been identified and removed from harm as a result of the 12th Victim Identification Taskforce organised by...

More ›››

Important Facts

2024

Operations

69+

Evidence

1961+

Cases

445+

Child Sexual Abuse

208+

National CSIRT-CY

Συμβουλές για Ενίσχυση της Ψηφιακής Ασφάλειας κατά την Διάρκεια των Ηλεκτρονικών Αγορών της Black Friday και Cyber Monday

Wednesday, November 12, 2025

️ Συμβουλές για Ενίσχυση της Ψηφιακής Ασφάλειας κατά τη διάρκεια των ηλεκτρονικών αγορών της Black Friday και Cyber Monday

More ›››

Ψηφιακή Ασφάλεια για Ηλικιωμένους: Συμβουλές από τον Επίτροπο Επικοινωνιών - Αρχή Ψηφιακής Ασφάλειας

Wednesday, March 12, 2025

Η ψηφιακή εποχή που ζούμε προσφέρει αμέτρητες δυνατότητες, αλλά και σημαντικές προκλήσεις, ιδιαίτερα για τους ηλικιωμένους που μπορεί να είναι πιο ευάλωτοι σε διαδικτυακές απειλές. Το Γραφείο Επιτρόπου Επικοινωνιών - Αρχή Ψηφιακής Ασφάλειας παρέχει χρήσιμες συμβουλές για ασφαλή πλοήγηση στο διαδίκτυο.

More ›››

Εργαλείο GetSafeOnline

Thursday, November 28, 2024

Το Γραφείο Επιτρόπου Επικοινωνιών - Αρχή Ψηφιακής Ασφάλειας, με γνώμονα την προστασία των πολιτών και των χρηστών διαδικτύου, έχει αναπτύξει μία πρωτοποριακή πλατφόρμα ανίχνευσης πιθανής διεύθυνσης ηλεκτρονικού «ψαρέματος».

More ›››

Ανακοίνωση Αρχής Ψηφιακής Ασφάλειας

Friday, October 18, 2024

Η Αρχή Ψηφιακής Ασφάλειας λαμβάνει σοβαρά υπόψη και αξιολογεί τις πληροφορίες για κυβερνοεπιθέσεις και ενημερώνει τις ουσιώδεις υπηρεσίες για τη λήψη κατάλληλων προληπτικών μέτρων στο πλαίσιο των αρμοδιοτήτων της.

More ›››

Απλές και καθημερινές συμβουλές ασφάλειας στον κυβερνοχώρο για τα παιδιά και τους γονείς

Tuesday, February 13, 2024


Η έκθεση των παιδιών μας στις ψηφιακές τεχνολογίες από πολύ μικρή ηλικία προσφέρει, αφενός, ευκαιρίες και δυνατότητες για μάθηση και εκπαίδευση, εμπεριέχει, αφετέρου, κινδύνους για τους οποίους τα παιδιά πρέπει να ενημερώνονται και να μαθαίνουν να αντιμετωπίζουν.

More ›››

Πώς να ελέγξετε αν το τηλέφωνό σας έχει παραβιαστεί; 5 σημάδια για να καταλάβετε

Friday, November 17, 2023

Το κινητό σας τηλέφωνο αποθηκεύει πολλές προσωπικές πληροφορίες που θα μπορούσαν να
χρησιμοποιηθούν εναντίον σας αν πέσουν σε λάθος χέρια.

More ›››

CERT-EU RSS Feeds

2026-022: Critical vulnerabilities in Nginx

Wednesday, November 18, 2026
On 18 November 2026, F5 published an advisory addressing five vulnerabilities in NGINX that allow an unauthenticated remote attacker to execute code with the privileges of the NGINX worker process.
While researchers managed to successfully demonstrate the use of CVE-2026-123007, no exploitation in the wild has been reported yet.
It is recommended to swiftly update NGINX as soon as possible, prioritising internet facing appliances.
More ›››

2026-021: High Severity Vulnerability in Java SE and OpenJDK

Wednesday, November 18, 2026
On 17 November 2026, Oracle and the OpenJDK project released fixes for CVE-2026-114938, a high severity vulnerability in OpenJDK which could lead, under certain circumstances, in unauthenticated Remote Code Execution (RCE).
CERT-EU recommends updating vulnerable version of OpenJDK, prioritising internet facing applications.
More ›››

2026-020: Critical Vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway

Thursday, November 12, 2026
On 12 November 2026, the Cloud Software Group published security bulletins for its Citrix products addressing 28 memory flaws in Citrix NetScaler ADC and Citrix NetScaler Gateway. One of these vulnerabilities, CVE-2026-120868, affects every deployment, including those using the default configuration. The vendor bulletin describes the impact as unpredictable behaviour and denial of service.
Citrix reports no exploitation, and no public proof-of-concept has been confirmed. CERT-EU strongly recommends upgrading all customer-managed NetScaler ADC and NetScaler Gateway appliances to the fixed releases. Internet-facing Gateway and AAA appliances should be upgraded first.
More ›››

2026-018: Critical Vulnerabilities in PHP

Friday, October 23, 2026
On 20 October 2026, the PHP project announced an upcoming security release addressing two critical vulnerabilities in PHP. Public reports indicated that these vulnerabilities could lead to remote code execution (RCE).
The PHP team released the fixes today, 21 October 2026 at 13:30 UTC, in PHP versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Both vulnerabilities can allow unauthenticated remote code execution. Technical details are now being discussed publicly, and initial proofs of concept (PoCs) have begun to circulate. This raises the likelihood that attackers are already exploiting the vulnerabilities.
[New] On 23 October, PHP disclosed a new RCE vulnerability. However, it affects only web applications configured in an unusual way, and PHP considers it an unlikely risk. PHP will not issue an out-of-band release for this vulnerability. Instead, organisations are advised to apply mitigation to fully protect from this RCE vector.
CERT-EU advises organisations to patch affected assets immediately. Where that is not feasible, organisations should consider isolating internet-facing applications from public networks until a fix is applied and verified.
More ›››

2026-019: Critical Vulnerability in GitLab Community and Enterprise Editions

Thursday, October 22, 2026
On 21 October 2026, GitLab published a security advisory addressing several vulnerabilities among which a critical flaw that could allow an unauthenticated user to execute arbitrary code on a GitLab server.
CERT-EU recommends organisations to update affected assets as soon as possible, prioritising internet facing assets, and to run an assessment to identify compromised assets.
More ›››

2026-017: Critical Vulnerability in Cisco Secure Email Gateway

Thursday, October 15, 2026
On 14 October 2026, Cisco published a security advisory addressing a critical vulnerability affecting the Advanced Malware Protection (AMP) feature of Cisco Secure Email Gateway. This vulnerability could allow an unauthenticated, remote attacker to write arbitrary files and execute commands with root privileges on the underlying operating system.
The Cisco PSIRT is aware of active exploitation of this vulnerability.
CERT-EU strongly recommends updating the Content Scanner Tools package or upgrading Cisco AsyncOS Software to a fixed release as soon as possible, prioritising appliances reachable from the internet. CERT-EU also recommends checking all affected appliances for indicators of compromise.
More ›››
© Copyright 2026, Υποδιεύθυνση Ηλεκτρονικού Εγκλήματος, All Rights Reserved
Design & Development by Digital Forensic Lab | Hosting by Network Solutions LTD